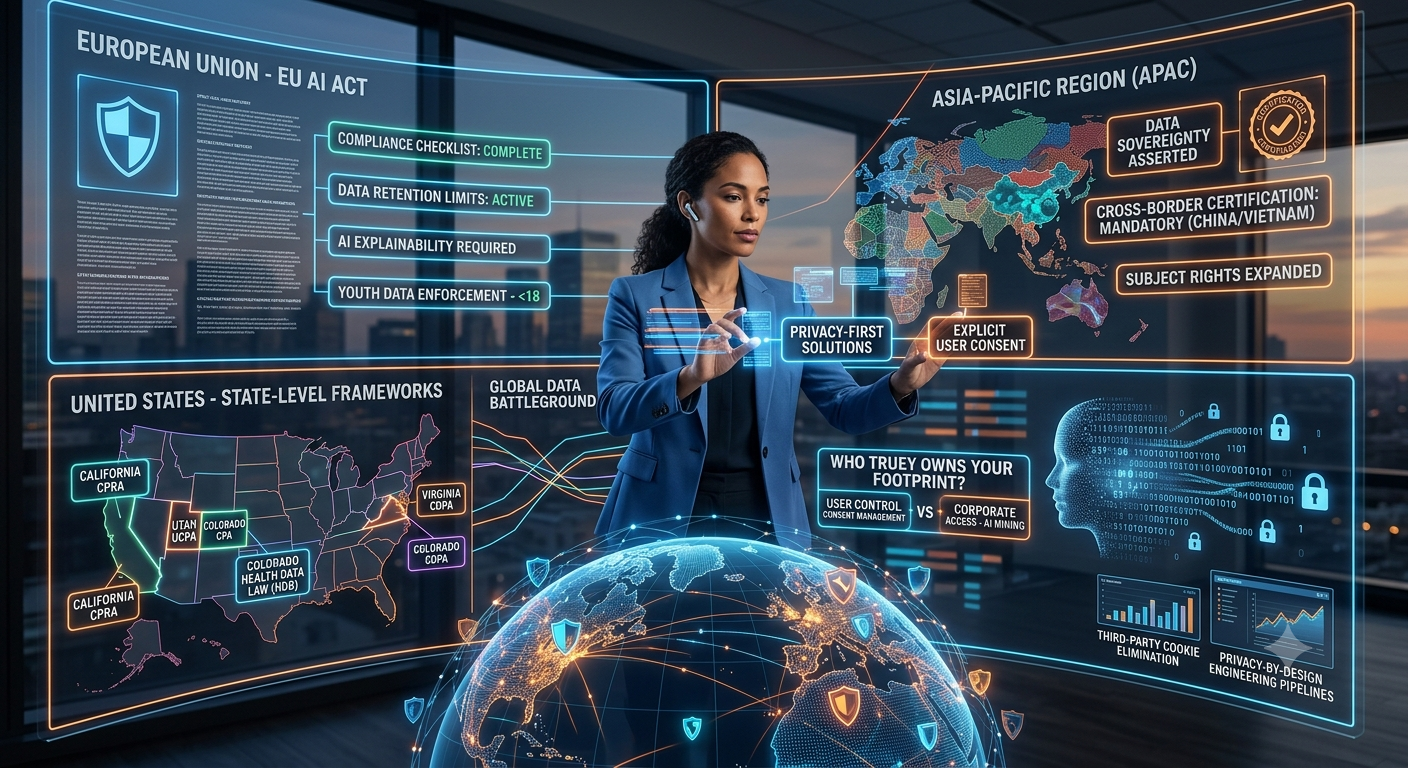
For much of the internet's history, businesses operated under the assumption that the digital world was largely borderless. Companies could collect, process, and transfer data across countries with relatively few restrictions, allowing global platforms to scale rapidly. Today, that landscape has changed dramatically. Governments around the world are introducing increasingly complex data protection laws, digital sovereignty policies, and artificial intelligence regulations that are reshaping how organizations manage information.
The vision of a single, unified digital ecosystem is gradually giving way to a fragmented regulatory environment where every region follows its own legal framework. Organizations operating internationally must now navigate a growing network of overlapping privacy laws, cybersecurity requirements, AI regulations, and cross-border data transfer restrictions. As a result, data governance has become one of the most significant strategic challenges facing modern enterprises.
This regulatory transformation is being driven by two major forces. First, governments are seeking greater control over the personal data generated by their citizens in order to strengthen privacy, national security, and digital sovereignty. Second, the rapid expansion of generative artificial intelligence has dramatically increased the demand for high-quality data, raising new concerns about how information is collected, processed, and used to train increasingly powerful AI systems.
Major Compliance Milestones Shaping the Digital Economy
Organizations operating across multiple markets must stay informed about rapidly evolving regulatory developments that continue to redefine global compliance obligations.
The European Union's AI Act
The European Union has introduced one of the world's most comprehensive regulatory frameworks for artificial intelligence through the AI Act. Following its phased implementation, the legislation establishes strict requirements for organizations developing or deploying AI systems.
Companies must maintain detailed documentation of AI training data, risk management processes, model transparency, and decision-making mechanisms. High-risk AI systems are subject to extensive oversight, while organizations that fail to comply may face significant financial penalties. The regulation reflects a broader international movement toward greater accountability and responsible AI governance.
Expanding Regional Data Protection Laws
Privacy regulation is expanding well beyond Europe. Across the Asia-Pacific region, governments are strengthening legal protections for personal data while introducing stricter requirements for organizations handling sensitive information.
Countries are implementing enhanced data subject rights, stronger consent requirements, tighter cybersecurity obligations, and more rigorous controls over international data transfers. These developments require multinational organizations to adapt compliance strategies to accommodate regional legal differences rather than relying on a single global privacy model.
The Growth of State-Level Privacy Laws in the United States
Unlike many jurisdictions that operate under a unified national privacy framework, the United States continues to develop privacy regulation primarily at the state level. Individual states have introduced their own legislation governing consumer privacy rights, data collection practices, and organizational responsibilities.
For businesses operating nationwide, this creates additional complexity. Companies must simultaneously comply with multiple state-specific requirements regarding consumer rights, data processing, breach notification, and transparency obligations, increasing both operational costs and compliance challenges.
Protecting Young People and Sensitive Data
One of the most significant areas of regulatory focus involves protecting children, teenagers, and other vulnerable groups in the digital environment.
Modern privacy laws increasingly require organizations to adopt "privacy and safety by design", meaning that digital products should incorporate protective measures from the earliest stages of development rather than adding them later.
Many regulations have expanded the definition of sensitive personal data to include information relating to teenagers and young users, introducing stricter age verification requirements, stronger parental protections, limitations on behavioral advertising, and tighter restrictions on how long personal information may be retained.
These changes reflect growing concerns about social media usage, targeted advertising, online safety, and the long-term collection of personal data belonging to younger users.
The Shift Toward Privacy-First Data Strategies
The digital advertising industry is also undergoing significant transformation. The gradual elimination of third-party tracking cookies by major web browsers is changing how organizations collect and utilize customer information.
Rather than relying on extensive third-party tracking, businesses are increasingly adopting privacy-first approaches that emphasize first-party data, transparent consent mechanisms, server-side data processing, and data minimization principles. These strategies allow organizations to deliver personalized services while reducing unnecessary data collection and strengthening user trust.
For many companies, privacy is no longer viewed solely as a legal obligation. Instead, it has become an important competitive advantage that strengthens customer confidence and supports long-term digital sustainability.
Empowering Individuals Through Better Data Control
As digital services become more integrated into everyday life, individuals are also gaining greater responsibility for protecting their own personal information.
Practicing good digital hygiene includes reviewing privacy settings regularly, using privacy-focused browsers and search engines where appropriate, limiting unnecessary data sharing, carefully managing cookie consent preferences, enabling multi-factor authentication, and periodically deleting unused online accounts that continue to store personal information.
Many modern privacy regulations also provide users with expanded rights, including the ability to access personal data, correct inaccurate information, request deletion of unnecessary records, and understand how organizations process their information. Exercising these rights helps individuals maintain greater control over their digital identities.
Looking Ahead
The future of digital governance will be defined by increasing regulatory diversity rather than global uniformity. Organizations can no longer assume that a single compliance strategy will satisfy every jurisdiction. Instead, they must build flexible privacy programs capable of adapting to changing legal requirements across multiple regions.
Businesses that successfully integrate privacy by design, responsible AI governance, strong cybersecurity practices, and transparent data management into their operations will be better positioned to earn customer trust, reduce regulatory risk, and remain competitive in an increasingly complex digital economy.
Ultimately, data privacy is no longer simply an IT or legal issue—it has become a strategic business priority. In a world where digital borders continue to evolve, the organizations that treat privacy as a core element of innovation rather than a compliance burden will be best equipped to thrive in the next generation of the global digital economy.